The agent closes the loop with the scanner
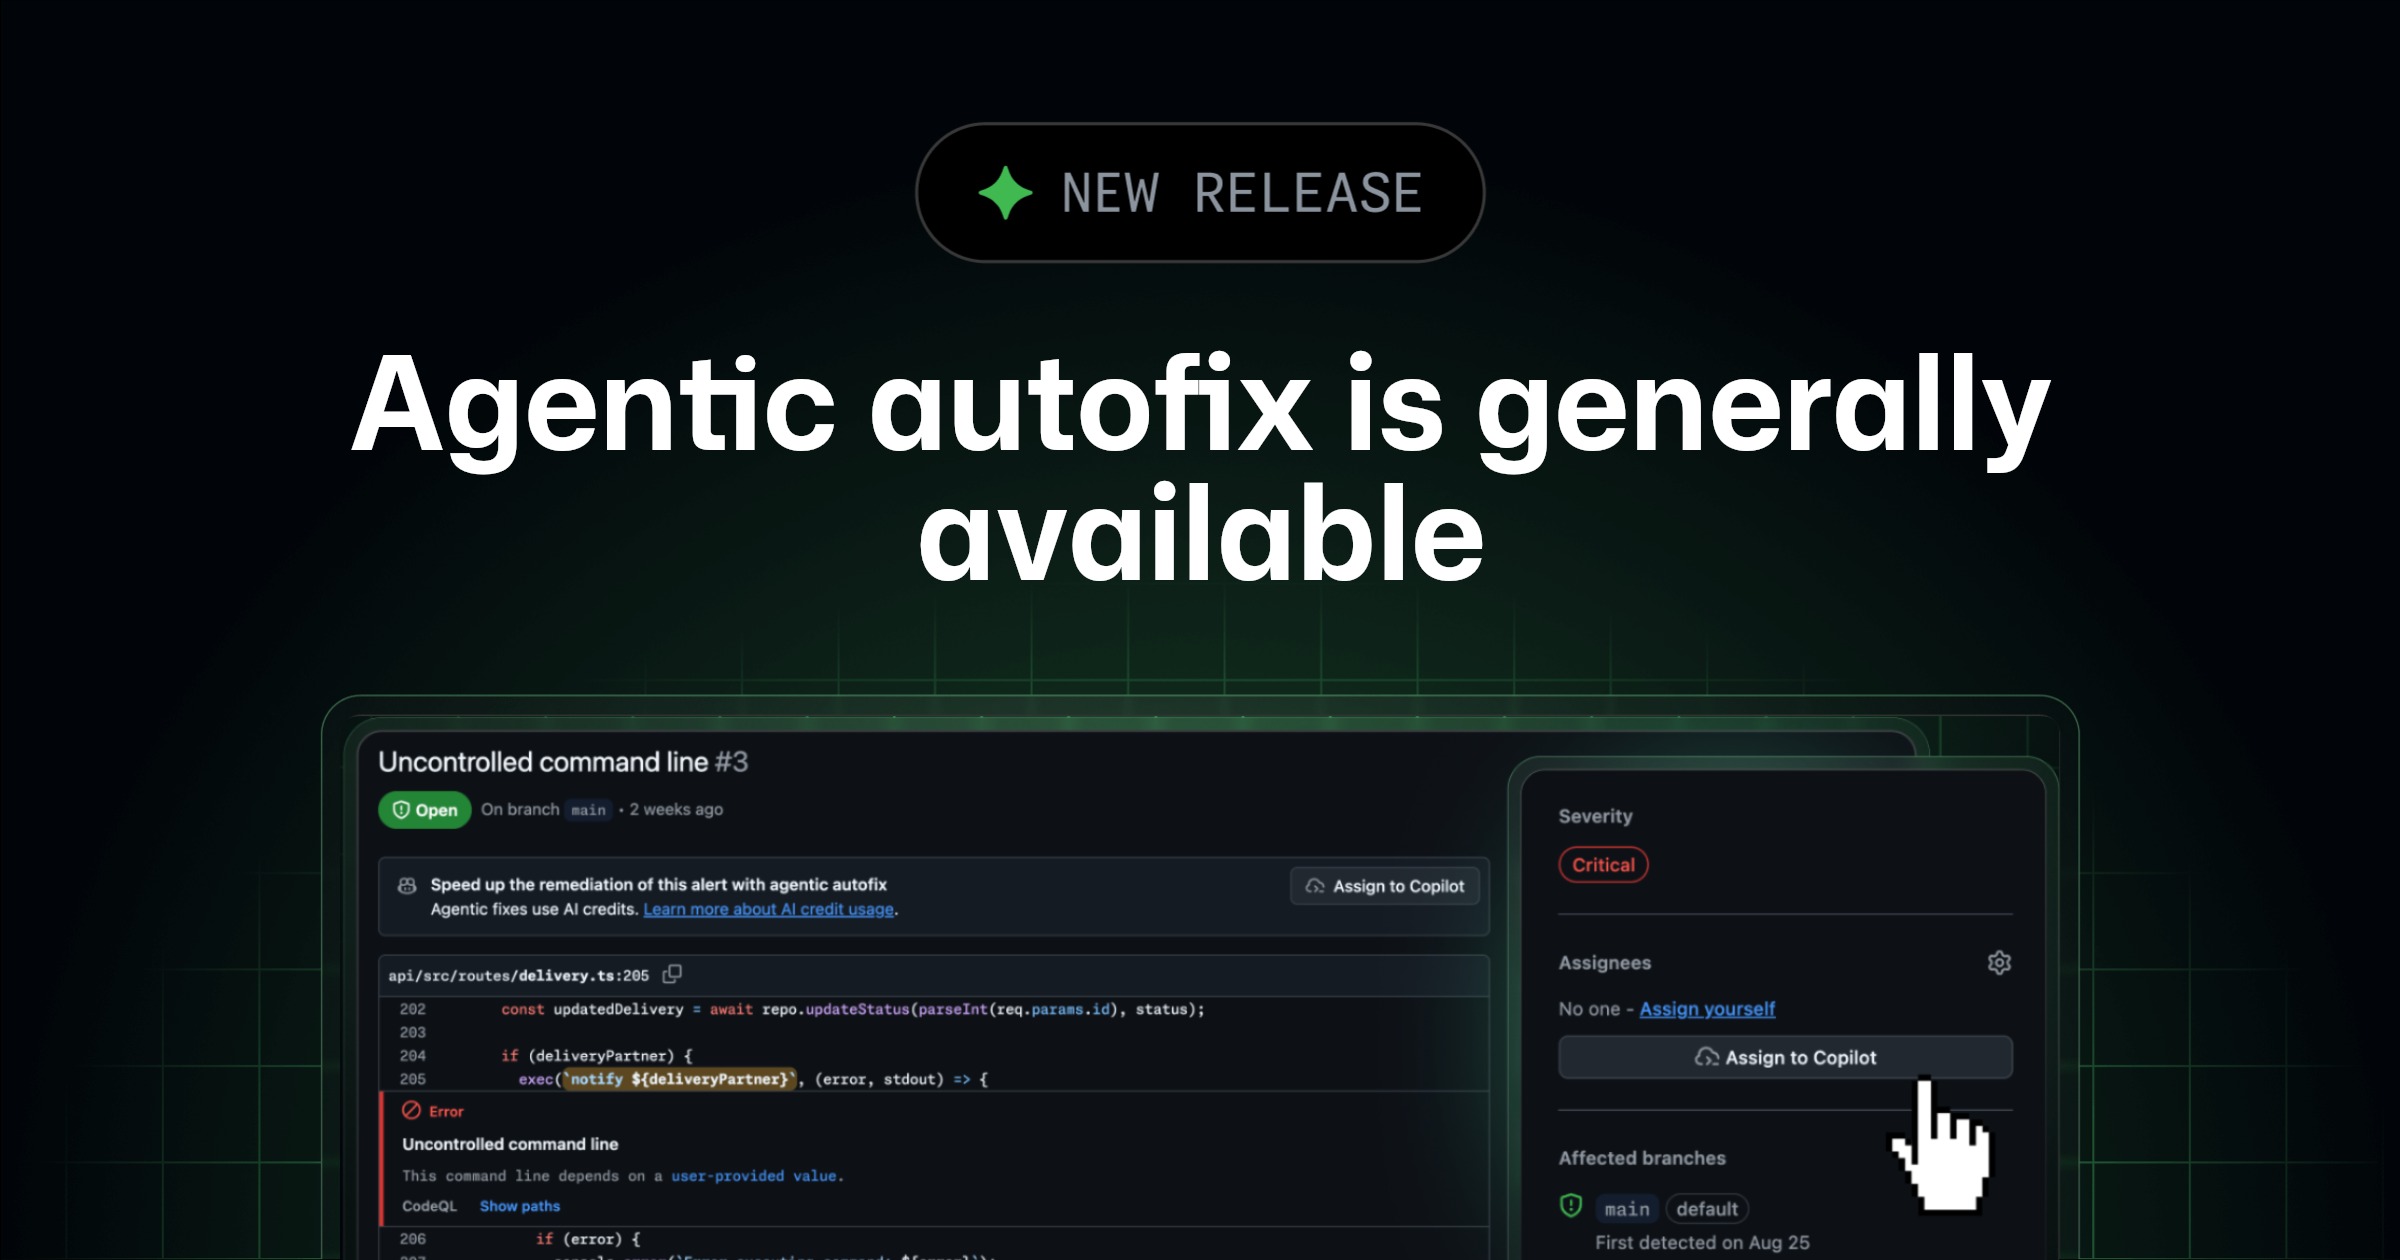
GitHub’s agentic autofix for code-scanning alerts is generally available. Assign an eligible CodeQL alert to Copilot and it explores the relevant files, proposes a change, reruns CodeQL, iterates if needed, and opens a draft pull request. The PR summarizes why the fix should close the alert and what validation ran.
That verification step is the notable change. A generated patch can look plausible while missing a related path or introducing a new issue. Re-running the same analyzer before asking a developer to review creates a tighter loop than simply producing a code suggestion. GitHub says an administrator can assign up to 25 alerts together in one pull request.
It is a review assistant, not an automatic security merge
The feature supports alerts on the repository’s default branch; alerts found only on pull requests or other branches are not eligible. The draft PR remains for a developer to inspect and approve. GitHub says Agentic Autofix is available to GitHub Code Security and GitHub Advanced Security customers on Enterprise Cloud, and an enterprise administrator must enable the policy. Copilot billing is also required.
For a security team, the practical question is whether the proposed change actually resolves the vulnerable path and survives broader tests—not just whether CodeQL’s original alert disappears. The feature automates investigation and first-pass repair, while the repository’s human review and deployment controls remain in the loop.
Source published 2026-10-15. Coverage is based on the maker’s announcement and demonstration.