Taskflows turned a general model into a targeted mobile audit
GitHub Security Lab researcher Kevin Stubbings reports that targeted AI taskflows found and reported 24 Android application vulnerabilities. The open-source Taskflow Agent packages prompts and workflows so a model can work through a security audit in smaller, directed steps instead of receiving one broad request to “find bugs.”
The method first identifies mobile entry points, then asks the model to consider vulnerability classes relevant to those components. The researcher says repeated runs helped surface complex issues that a single pass might miss. GitHub’s example workflow can take an hour or two on a medium-sized repository and requires a Copilot license with premium model requests.
Two findings show the potential impact
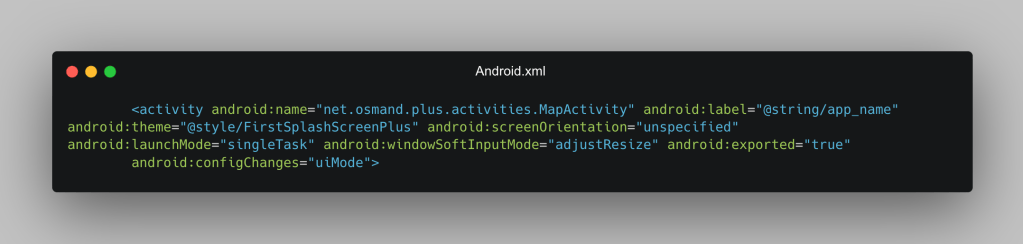
One reported OsmAnd issue involved an exported Android activity that accepted untrusted intent extras. The research write-up says another app could use the pathway to alter map settings and expose location-related data. A second example chained a Wikipedia Android deep-link parsing bug with a WebView cookie issue into a potential account-takeover path. GitHub says those examples had already been disclosed when the article was published.
These are security-research findings described by the team—not evidence that the taskflow autonomously exploits live users. The report is about locating code paths for researchers to investigate and disclose responsibly.
The researcher still decides what is real and severe
GitHub explicitly notes that language models can misjudge severity and report false positives. The researcher had to verify findings, account for mitigating conditions and in some cases create proof-of-concept tests. The taskflows are designed to accelerate that work, not replace the security review that determines whether a report is valid.
The project is open source, so other teams can inspect the taskflows and adapt them to their own repositories. For maintainers, the practical payoff is a repeatable, targeted first pass that can help a small security team cover more application code.
Source published September 28, 2026. Coverage is based on the maker’s announcement and demonstration.